

How to Monitor Third-Party Data Sharing


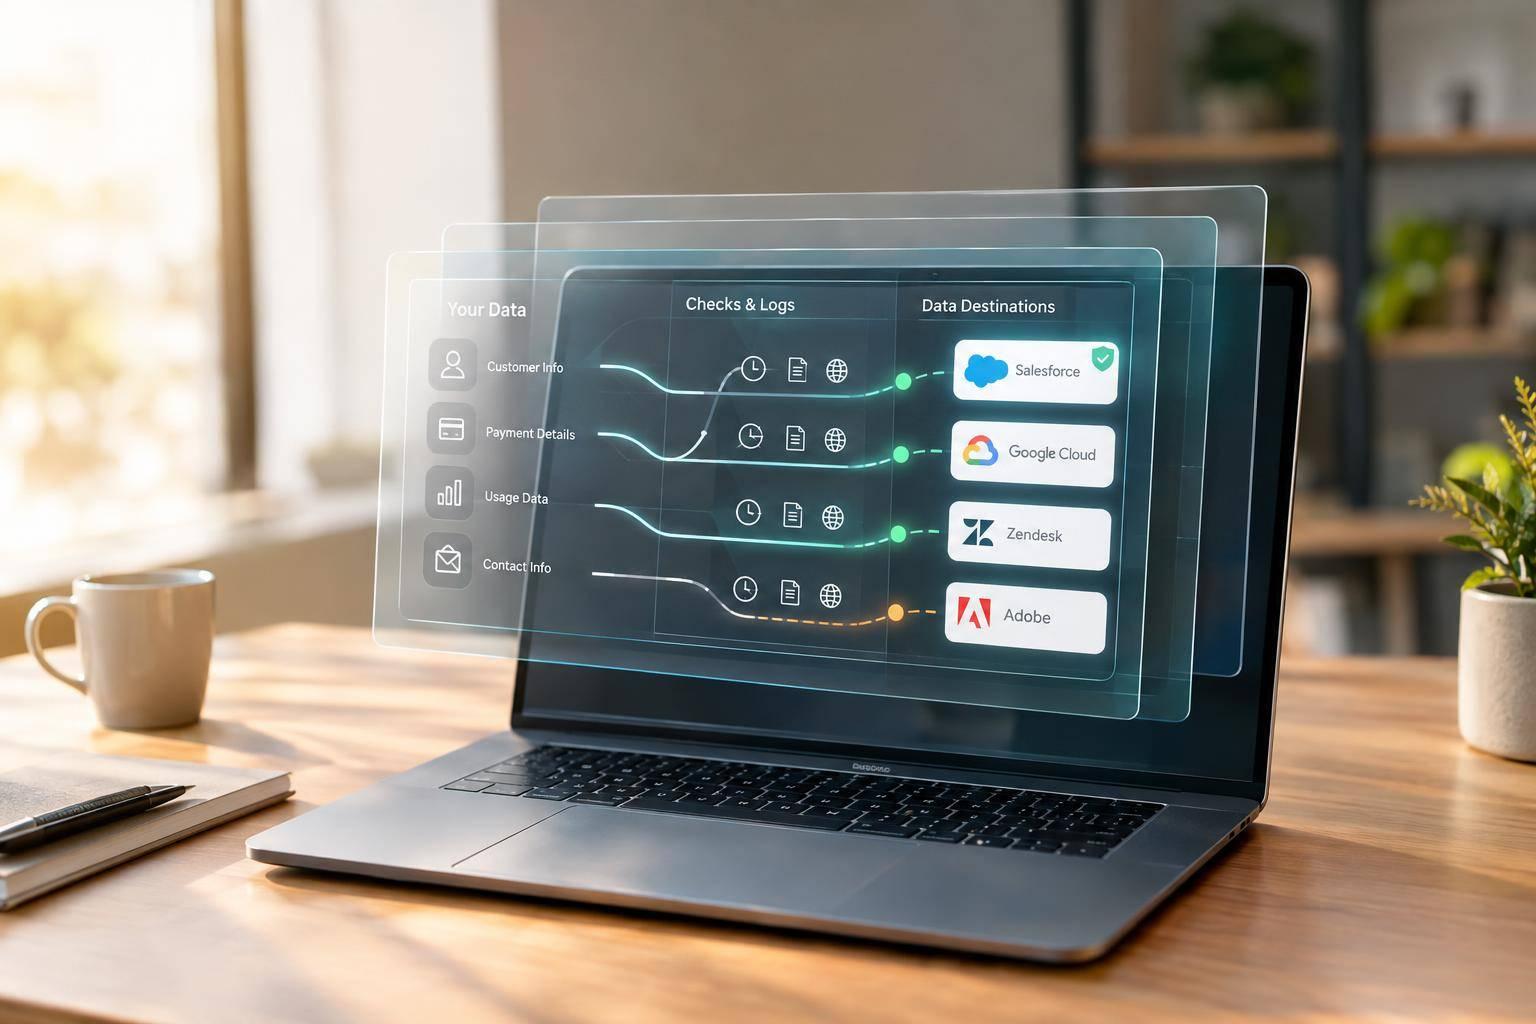
I monitor third-party data sharing by comparing actual transfers with approved fields, destinations, and permissions - not just checking that a connection works. I log transfer metadata, keep lead details and credentials out of logs, and assign someone to investigate alerts.
My checklist covers 3 steps:
- Map approved sharing: Record vendors, form routes, data fields, access rights, retention rules, and owners.
- Track activity: Review transfer and access logs, test alerts, and set thresholds based on normal traffic.
- Resolve gaps: Review permissions, trace failed requests and retries, and require approval before sharing changes.
The limit? <u>Logs show recorded activity, not everything a vendor does.</u> I pair them with access, contract, and deletion checks, revisit vendors when risks change, and require validation before closing issues. A 1-hour triage target for suspected unapproved sharing is an internal response goal, not a legal notification deadline.

How to Monitor Third-Party Data Sharing
1. Map Vendors, Data Fields, and Approved Access
Document Each Vendor’s Data Use and Owner
Start with the approved map - not the logs. Build a vendor register for every CRM, enrichment, validation, analytics, or automation connection. Record each vendor’s business purpose, approved fields, transfer method, processing locations, subprocessors, retention period, deletion process, contract status, and internal owner.
Give each transfer path its own row. Include the source, destination, direction, expected frequency, and approved environment. This register lets you compare approved sharing with actual activity later.
Approval must cover the data use - not just the connection. Identify personal information, inferred attributes, and consent records. Check that contracts and privacy notices cover sharing, onward sharing, and deletion. Mark unclear or unsigned arrangements pending review. Save the approved map with its version, approval date, and supporting agreements, then use it as the baseline for log and permission reviews.
Map Reform Form Data to Its Destinations
For each Reform form, record every field’s type, required status, display condition, destination, and reason for sharing. Include hidden fields when used. Map conditional routes and enrichment separately, noting the inputs sent, attributes returned, and downstream fields updated. Every recipient needs a documented reason to receive each field.
If you store incomplete responses, map them as a separate path. Record where they stay, whether they reach connected systems, and how retention and deletion rules apply.
Test each route with synthetic submissions. Check that uncollected optional fields stay absent and consent records reach the intended destination. Save the results with the approval record. Then match each destination to the users, tokens, and permissions that can reach it.
List Users, Tokens, and Permissions
Register employees, integration administrators, service accounts, API keys, OAuth grants, and webhooks as separate access paths. For each path, record its owner, purpose, scope, permitted fields, permitted actions, environment, creation date, last review date, expiration or rotation date, and revocation method. Store only a credential reference - not the credential itself.
Limit access by field, operation, and environment. If controls can’t enforce those limits, document the gap. Use the access list to catch changes before they lead to unapproved sharing. Require a review before adding destinations, fields, or broader permissions.
sbb-itb-5f36581
2. Set Up Logs, API Monitoring, and Alerts
Record Transfer Details and Logging Gaps
Start log reviews with the approved vendor map and access list. Store integration, identity, API, and vendor audit logs in one access-controlled location.
For each transfer, record the vendor, acting identity, timestamp and time zone, destination, endpoint or operation, data category, record count, result, and request ID. Keep administrative changes separate from data reads and writes. Use request IDs to link failed attempts to successful retries.
Check each tool’s logging requirements, and document missing event types and known evidence gaps. Don’t log full lead payloads or credentials. Limit access to logs that contain personal information.
Set and Test Activity Alerts
Set alerts for new destinations or credentials, unusual export volumes, unapproved data fields, access by inactive users, activity from unexpected regions or at unexpected times, and disabled logging or missing records. Compare activity against normal traffic, accounting for expected campaign spikes.
Give every alert a named responder and escalation path. Test with synthetic events - not real lead data - to check that alerts trigger and reach the right owner. Document alerts that can’t work because the required evidence isn’t available.
Assign Monitoring Owners, Thresholds, and Retention
Use the table below as a starting point for detecting activity outside the approved destinations, fields, and permissions for each mapped vendor path. The retention periods are planning suggestions. Confirm that each source provides the listed evidence.
| Event | Detection purpose | Available evidence to check | Alert owner | Alert threshold | Starting retention |
|---|---|---|---|---|---|
| API calls | Detect volume spikes | Endpoint, record count | Integration owner | Above baseline after campaign adjustment | 90 days |
| Authentication events | Identify access without approval | Identity, IP, region | Security | Any inactive-user access | 1 year |
| Configuration changes | Spot new destinations | Admin ID, change log | Integration owner | Any unapproved change | 1 year |
| Failed requests | Trace integration breaks | Error code, request ID | Integration owner | Failure rate above baseline | 30 days |
| Data exports | Prevent bulk exfiltration | Record count, destination | Security | Unusual bulk threshold | 2 years |
| OAuth activity | Monitor token usage | Token ID, scope | Identity administrator | New credential creation | 1 year |
Base thresholds on observed activity, not fixed percentages. Include scheduled exports and campaign traffic in the baseline. Treat unapproved destinations or permissions as exceptions at any volume.
Set retention periods according to risk and legal or contractual requirements. Review both thresholds and retention when traffic, data use, or contract terms change.
Episode 28 - Manage privacy in third-party data sharing with clear boundaries and controls (Domai...
3. Review Access, Changes, and Failed Requests
After reviewing alerts and logs, check that access still matches the approved register.
Check Permissions and Approve Data-Sharing Changes
Compare current vendor access with the approved register after staffing or vendor changes. Remove outdated permissions when roles change. At offboarding, disable access, tokens, and sessions. Use named identities so each action can be traced to a person.
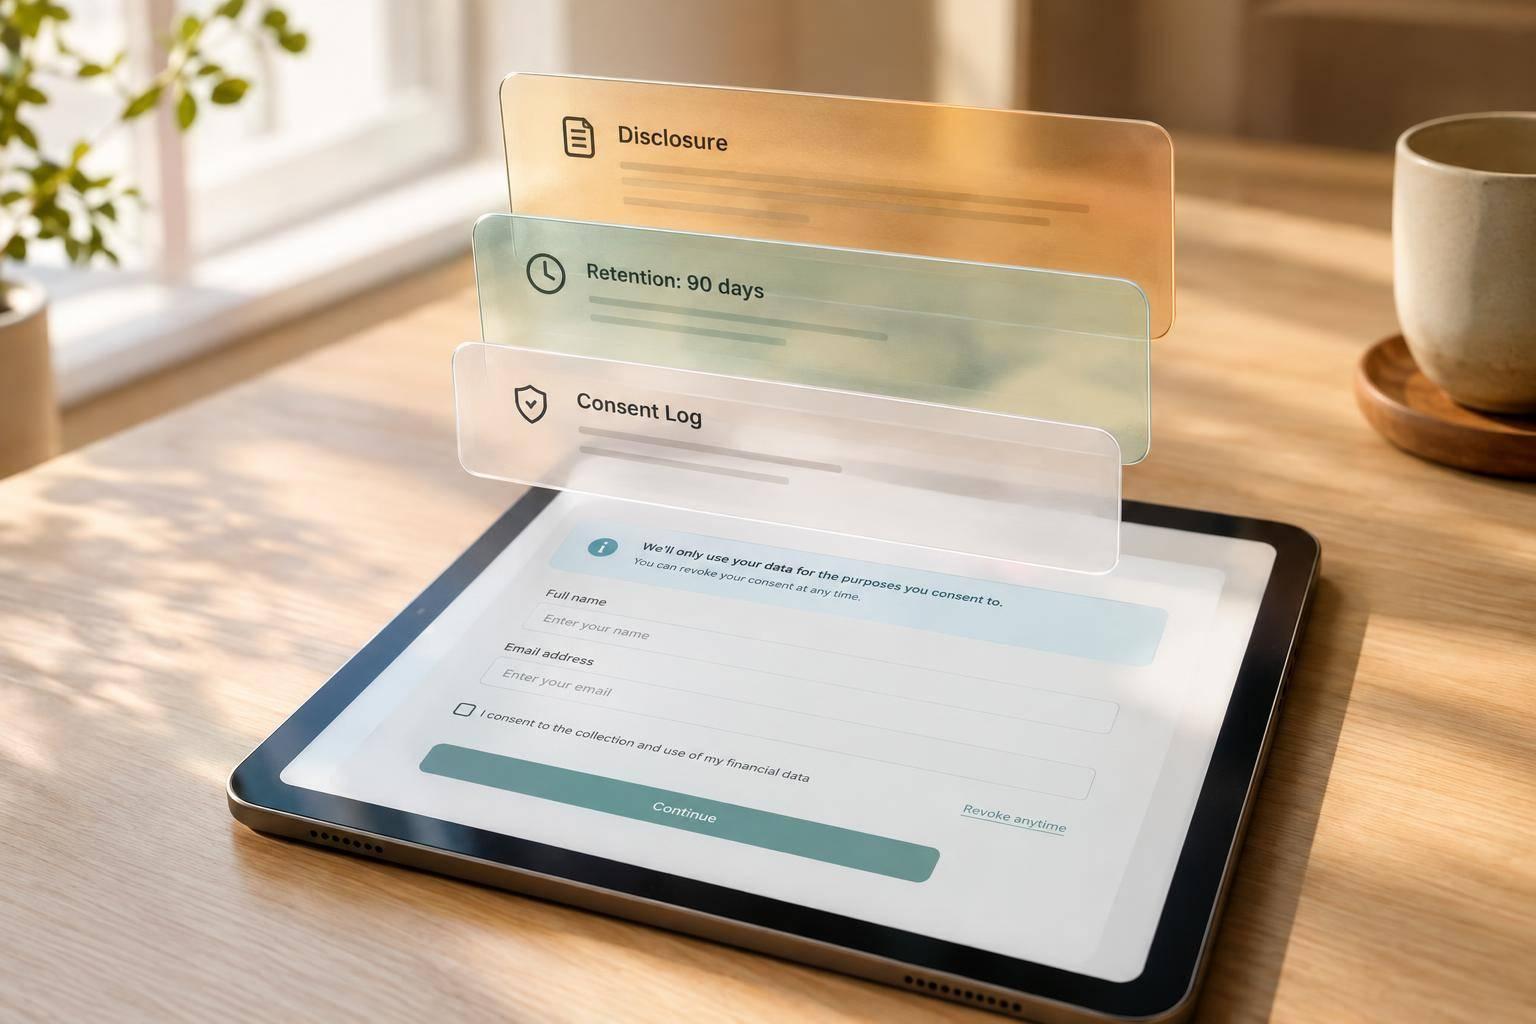
Require an approved privacy change ticket before expanding sharing. Record changes in the approved vendor map and get signoff from named business, technical, and privacy approvers. Check subprocessor changes against the data map and vendor contracts. Record any required approval before sharing starts.
Trace Failed Requests and Later Successes
Use logs to classify failures as credential, scope, rate-limit, schema, or outage issues before treating them as possible misuse. Then trace retries to later successes. If retries receive new IDs, link them through correlation records.
A successful retry does not prove the original transfer was clean. Document any gaps that prevent confirmation instead of marking delivery as verified.
For Reform submissions, use form analytics only as context. Analytics can flag a problem, but downstream integration and vendor logs must verify what was sent. Analytics alone cannot prove which fields a vendor received or how it used them. Keep source and permitted-use tags attached to downstream lead records where supported, and investigate discrepancies before closing the review.
Define Escalation and Issue Closure Rules
Treat these as internal response targets, not legal notification deadlines. Escalate unexplained bulk access, suspected unapproved sharing, and deletion that cannot be verified. Restrict affected connections when warranted, preserve evidence, and involve security, privacy, or legal teams to assess notification duties.
Do not close an issue based on vendor assurance alone. Require technical evidence and a successful validation test. Use the targets below to triage exceptions, and close them only after validation.
| Event | Severity | Owner | Response target | Evidence to preserve | Closure criteria |
|---|---|---|---|---|---|
| Routine sharing change | Low | Business, technical, and privacy approvers | Before enabling the change | Approval ticket; before-and-after config | Approved; map updated; test passes |
| Isolated failure | Low | Integration owner | Promptly | Error logs; timestamps; request and correlation IDs | Success confirmed or cause fixed |
| Repeated failures | Medium | Integration owner; security if unexplained | Promptly | Failure history; access and configuration records | Cause fixed; retries reconciled; validation passes |
| Unusual export | High | Security lead | Immediate triage; target within 1 hour | Export metadata; identity and session logs | Authorization confirmed or incident contained; affected records identified |
| Suspected unapproved sharing | High | Security and privacy leads; legal | Immediate escalation; target within 1 hour | Transfer records; approvals; data-flow maps | Sharing contained; scope assessed; notification decision documented; deletion evidence reviewed where required |
Conclusion: Set a Regular Vendor Review Schedule
After reviewing logs, alerts, and the access list, assign one owner to keep the transfer map and review calendar up to date. Include input from service, security, privacy, legal, and procurement owners.
Review outside the regular schedule when risk changes. Triggers include new subprocessors, security incidents, changes to destination-country laws, or changes to transfer methods.
At each reassessment, check the transfer map, logs, and deletion records to verify the approved purpose, subprocessors, incident contacts, and deletion procedures. Confirm that lead-form disclosures still match what the vendor actually does - not just what its policies say.
If contractual clauses or supplementary security measures no longer work, pause or update affected transfers immediately.
FAQs
How can I monitor vendors with limited audit logs?
Watch for duplicate CRM records, unexpected field values, and changes in junk submission volume. Use X-Request-ID or correlation IDs to trace API requests. Keep sync outcomes, status codes, and timestamps in a searchable audit trail.
Set alerts when sync error rates exceed 5% or success rates fall below 95%. Reconcile key CRM objects weekly, and run internal audits of high-risk areas each quarter.
How do I reduce false-positive sharing alerts?
Focus monitoring on a small set of high-priority metrics. Log skipped actions, partial successes, and validation failures separately so failure rates stay clear.
Use structured logs with correlation IDs to track each lead across your systems, pinpoint failures, and separate actual problems from expected behavior. Give every alert a clear owner so someone can investigate and fix the issue promptly.
How often should I review vendor access?
Review vendor access on a recurring, risk-based schedule. Reconcile CRM objects weekly, and audit API usage and field mappings monthly. Run in-house audits of high-risk areas quarterly, full audits annually, and independent reviews every 1–2 years.
Review access immediately after material changes, such as deploying a new form or tracking tag, or when market requirements change. Match review schedules to risk tiers to keep oversight consistent across integrated tools.
Related Blog Posts
Get new content delivered straight to your inbox

The Response
Updates on the Reform platform, insights on optimizing conversion rates, and tips to craft forms that convert.

Drive real results with form optimizations
Tested across hundreds of experiments, our strategies deliver a 215% lift in qualified leads for B2B and SaaS companies.
