

How Financial Data Rights Shape Form Design


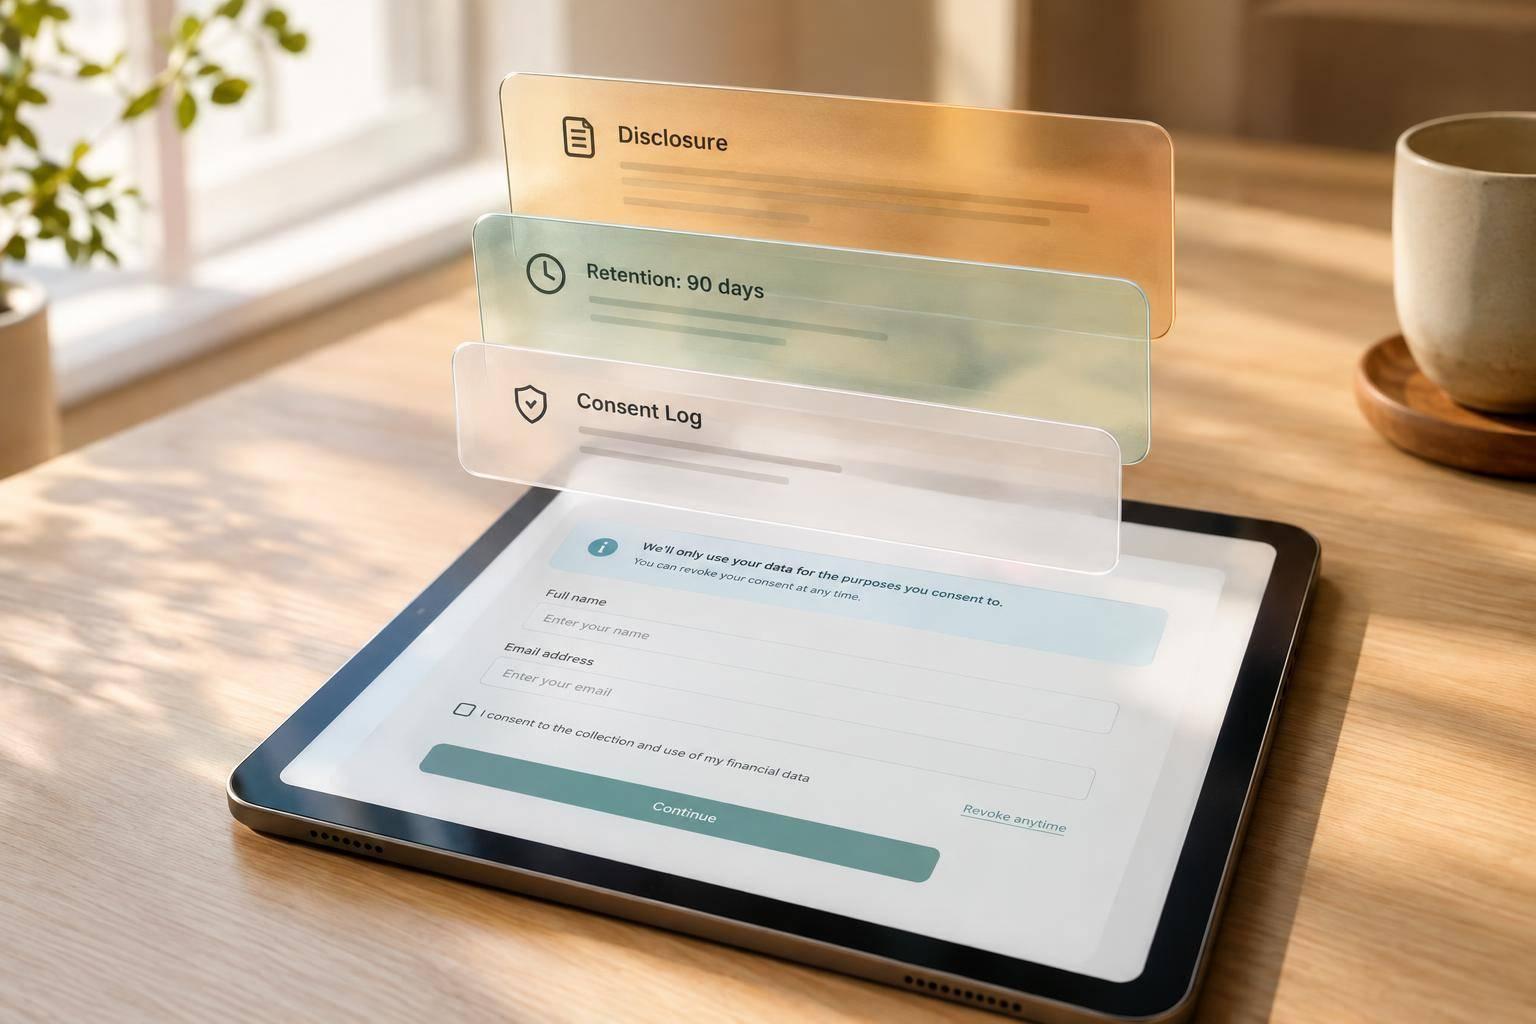
I design financial forms with four checks: collect less, explain access, disclose before consent, and track what happens next. For example, I ask for an income range instead of an exact figure when that meets the service’s needs.
My checklist covers both the form and the systems behind it:
- Check the rules: Section 1033 data-access rules and GLBA privacy duties serve different purposes.
- Limit data: Give each field a purpose and retention period, including data sent to other systems.
- Explain permission: State who gets the data, why, for how long, and how users can revoke access - before they agree.
- Track follow-through: Link consent, fulfillment, expiration, revocation, and deletion records with one request ID.
<u>A checked box is not the finish line.</u> I also test whether access ends when it should and whether required records remain. Because the article reports that the CFPB rule is stayed and under review as of October 16, 2026, I would verify its status before relying on its deadlines.

Financial Form Design: Four Data-Rights Checks
How Open Banking Works To Enhance Bank Application Security
sbb-itb-5f36581
Over-Collection: Remove Fields You Do Not Need
Once the rule is clear, remove any field that does not support the authorized use. Each extra field adds to what users must share and what the business must protect.
Map each field to a required purpose, then track where that data goes downstream. Full account numbers, exact income figures, and complete transaction histories may reveal more than a form needs. Identify the decision each field supports and document the rule or business need behind it. Remove fields with no defined need, and separate optional marketing or profiling data from the data needed to deliver the service.
Find Lower-Data Options for Financial Fields
Ask for the least precise data that still supports the decision. What works depends on the service and its verification requirements.
| Financial field | Legitimate use | Collection risk | Lower-data option |
|---|---|---|---|
| Income | Eligibility assessment | Too much personal detail | Income range when sufficient |
| Account identifiers | Ownership verification | Full identifier exposure | Verification result or masked ID |
| Transaction history | Cash-flow assessment | Irrelevant purchase details | Date range or totals only |
| Payment details | Authorized payment | Unneeded storage or reuse | Tokenized payment reference |
For transaction history, 24 months covers the authorized use in many cases. But that is not a reason to request a full itemized history on every form. Ask only for the period and level of detail the authorized service needs, subject to applicable requirements.
Limit Questions and Set Retention Periods
Multi-step forms and conditional routing can keep later questions hidden until earlier answers justify asking them. Hiding a question does not enforce collection or storage limits. Connected systems still need rules for storage, deletion triggers, and handling revocation.
Do not copy sensitive values into every integration. Pass a verification result or reference when that is enough. Set retention periods, deletion triggers, and revocation actions across all receiving systems.
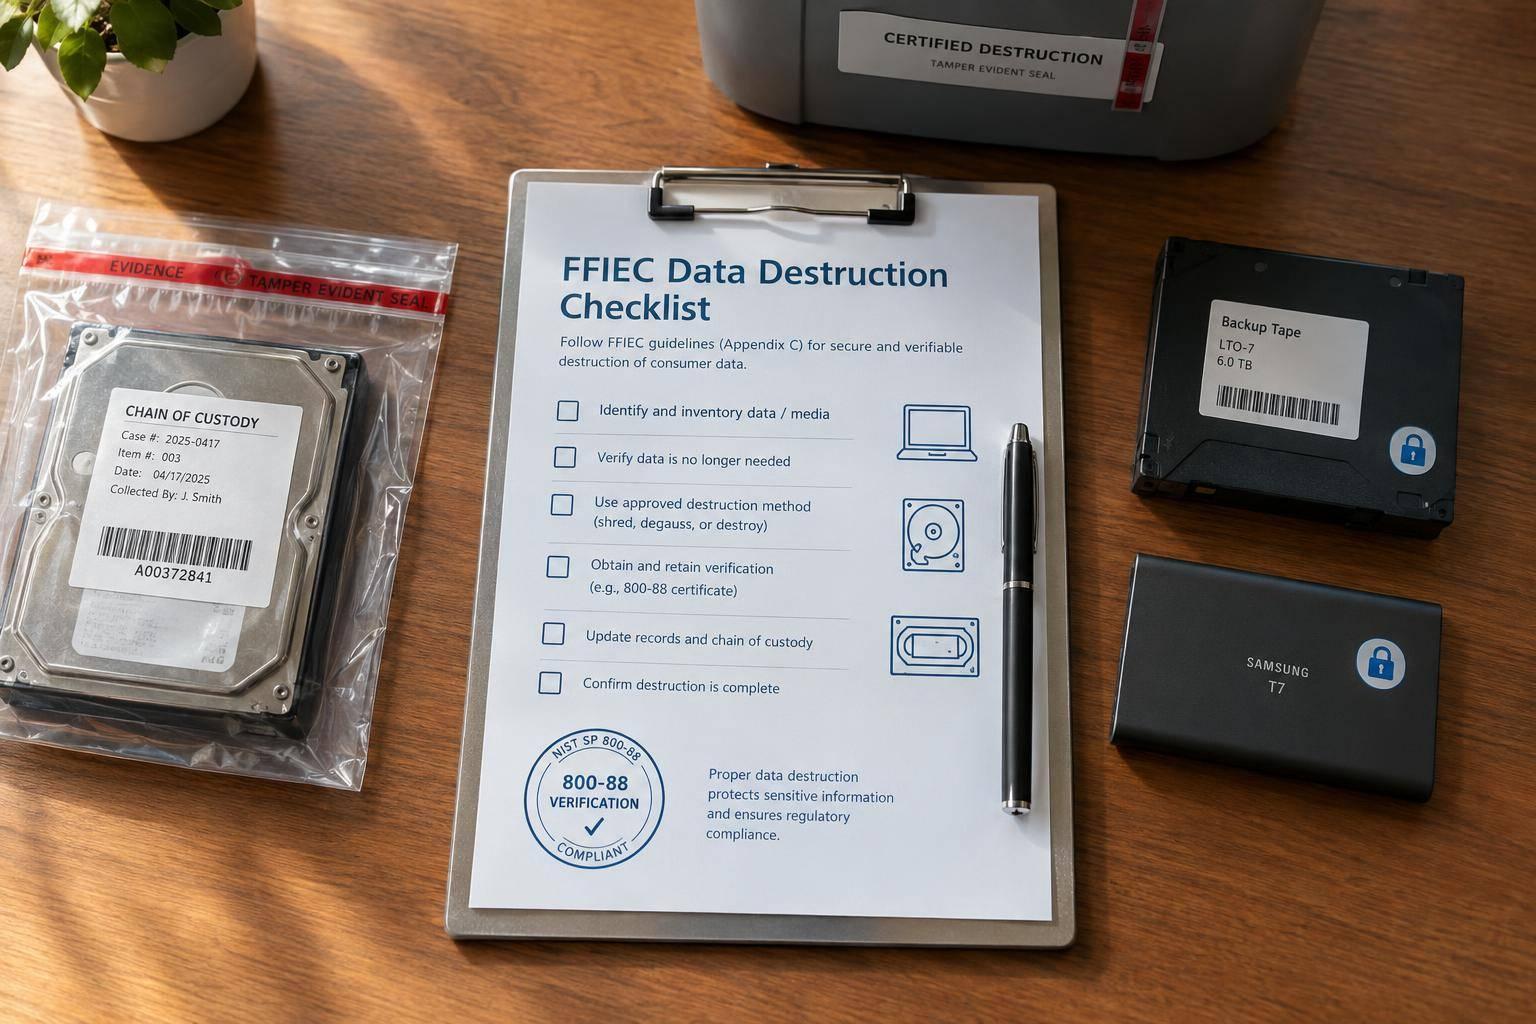
Revocation stops future collection. Deletion removes stored data unless retention is required. Keep request, authorization, and revocation logs separate from financial data, and retain those logs for at least three years.
Vague Consent and Late Disclosures: Explain Before Users Agree
After trimming fields, make the data-access authorization just as specific. Keep it separate from general terms and optional permissions.
State Who Gets Data, Why, and for How Long
Before users consent, name the recipient and any data aggregator. Spell out which accounts or financial products are involved, what data you’ll access, why you need it, how long access lasts, and how users can revoke it. Under the CFPB Section 1033 rule, access is limited to one year without reauthorization.
Treat identity verification, payment initiation, and personalization as separate purposes - not one blanket permission. Give optional uses their own unchecked controls.
Place Disclosures Before Each Data Decision
Put the specific authorization text before each data request. Place the explanation immediately above sensitive-data fields, account-linking controls, and access or transfer requests. Include links to the relevant privacy notices explaining collection, sharing, and opt-out options.
Reform’s multi-step structure lets you place each explanation at the step where users make that decision. Confirmation supports advance disclosure; it doesn’t replace it. Use the confirmation page to recap the same recipient, scope, duration, and revocation details your team will log.
Weak Tracking: Connect Requests to Follow-Through
After the user agrees, the form needs a record showing what happened next. An email alert is not a complete authorization record. On its own, it cannot establish what the user approved or whether access later ended or expired. Use one durable request ID to link intake, fulfillment, revocation, and retention actions.
Log Authorization Details and Request Events
Under that ID, record the consumer or account ID, recipient, data categories, purpose, consent version, duration, and submission and fulfillment status. Include timestamped events for authorization, expiration, revocation, and completion.
Keep these logs access-controlled. Preserve status changes rather than overwriting them, so reviewers can trace each step without rebuilding the audit trail by hand.
Assign Owners and Route Requests
Send only the records needed to approved CRM or compliance workflows, and check the destination’s access controls first. Assign owners to handle failed transfers, exceptions, and revocations.
Do not close a revocation request when the notice is sent. Record the access-control change and downstream completion. Keep the record linked to the request through every handoff.
| Tracking area | Weak tracking | Documented workflow |
|---|---|---|
| Consent evidence | Checkbox value only | Consent version, scope, and timestamp |
| Request status | Inbox follow-up | Assigned owner and status history |
| Revocation | Ad hoc message | Logged event routed to access controls, with completion recorded |
| Retention | Indefinite storage | Scheduled review and recorded action |
| Audit readiness | Manual audit reconstruction | Access-controlled request history |
Conclusion: Review the Form Before Launch
Before launch, check the live form and connected systems for excess data collection, unclear consent, disclosures that appear too late, and gaps in tracking.
Test Fields, Disclosures, and Request Workflows
- Fields: Document why each financial field is needed, how it supports the service, and how long its data will be kept. Remove fields the service doesn’t need.
- Authorization: List the recipient, data source, data categories, purpose, duration, and method for revoking access.
- Disclosures: Check what users see before they act, including every branching path. Save the rendered version.
- Workflows: Test fulfillment, revocation, and expiration from start to finish. Confirm that revocation stops collection, use, and retention. Record each test result.
- Records and ownership: Assign an owner to each request path. Define which logs and authorization records remain after access ends, and align retention with applicable requirements.
FAQs
How do I balance data minimization with verification needs?
Collect only the information you need to identify a user or process a request. Use email validation to check accuracy and lead enrichment to verify identity without adding form fields.
For sensitive inquiries, use multi-factor authentication or request a government-issued ID. Don’t collect unrelated personal data. Explain why you need each piece of information, and keep forms limited to what’s needed to support compliance and user trust.
How should I update consent when data uses change?
When you change how you use data, check whether the user’s existing consent covers the new processing purposes. If it doesn’t, get new, explicit consent from the user.
Keep a reliable audit trail: record the date, time, and exact version of the consent request shown to the user. Make sure preference updates stay consistent across your CRM and marketing tools.
How can I verify revocation across connected systems?
Audit the entire data flow - not just the on-screen confirmation. Map every recipient of your form data, trigger an opt-out, and check that the restriction reaches every downstream system. Where possible, automate consent updates or deletion requests.
Log the date, method, and scope of each withdrawal. Test deletion workflows regularly, and compare your privacy disclosures with actual integration settings to confirm that sharing stops as required.
Related Blog Posts
Get new content delivered straight to your inbox

The Response
Updates on the Reform platform, insights on optimizing conversion rates, and tips to craft forms that convert.

Drive real results with form optimizations
Tested across hundreds of experiments, our strategies deliver a 215% lift in qualified leads for B2B and SaaS companies.
