

FFIEC Data Destruction Rules: Checklist


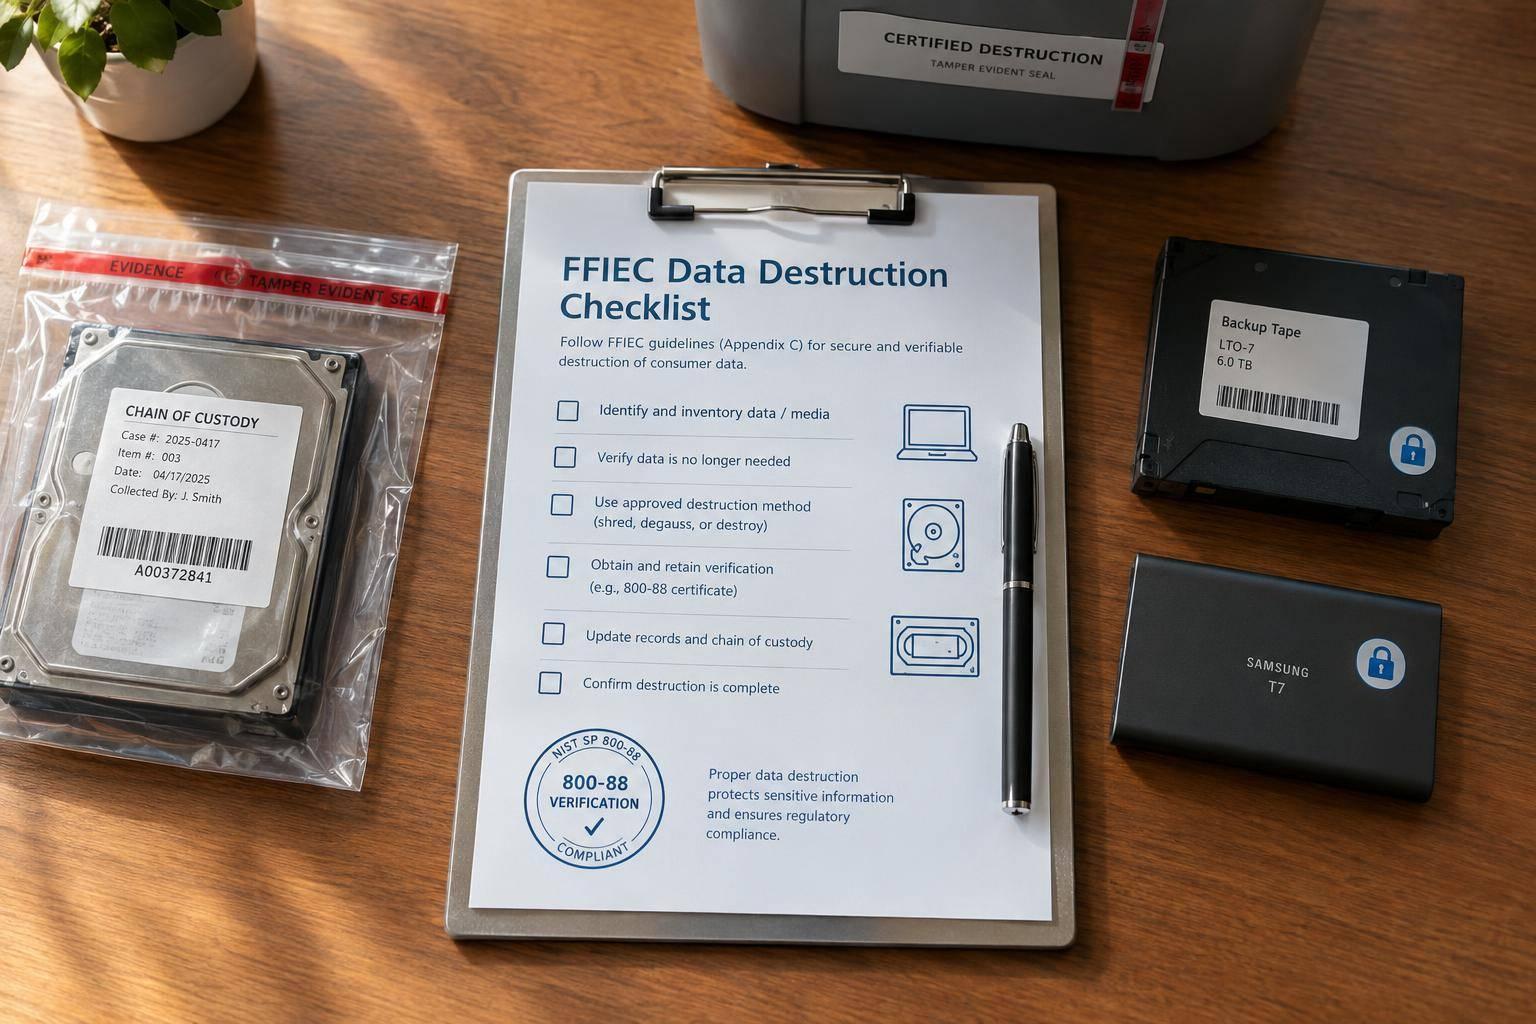
I don’t treat a destruction certificate as proof that disposal is complete. Before closing a batch, I check retention rules and legal holds, confirm destruction, and match the records to each asset or batch.
FFIEC guidance sets examiner expectations - it is not a disposal law. This checklist covers 5 areas I review:
- Scope and approval: Identify covered data, assign owners, and confirm what can be destroyed.
- Destruction methods: Match the method to paper, devices, media, and cloud copies; verify the results.
- Vendor controls: Check contracts, facilities, subcontractors, and every custody transfer.
- Disposal records: Reconcile inventories, approvals, destruction reports, and unresolved issues.
- Final sign-off: Confirm policy references NIST SP 800-88 Rev. 2 and close the file only after discrepancies are resolved.
My closing rule: <u>retired does not mean destroyed</u>. Your records need to show what happened - not just that equipment left the building.

FFIEC Data Destruction: 5 Control Checkpoints
NIST 800-88 Explained: Secure Data Destruction Guide
sbb-itb-5f36581
2. Paper, Device, and Media Destruction Checklist
After destruction is approved, choose a method that fits the medium and required assurance level.
Choose an Approved Method for Each Medium
☐ Set the required sanitization level before choosing a method. Follow NIST SP 800-88 Rev. 1 guidance and institutional policy. Account for data sensitivity, storage technology, and whether the media will be reused or discarded. Use Clear for overwriting, Purge for stronger resistance to recovery, and Destroy when the media must be unusable. Deleting files or reformatting alone is not sanitization. Use cryptographic erase only when destroying the keys makes the encrypted data unrecoverable.
| Medium | Risk | Approved method | Proof | Escalation trigger |
|---|---|---|---|---|
| Paper | Readable or reconstructable records | Shredding, pulping, or another process that prevents reconstruction | Inspection and destruction record | Readable remnants |
| SSDs | Data outside accessible storage areas | Purge, cryptographic erase, or physical destruction; never degaussing | Device-specific proof | Failed command or storage areas not covered |
| HDDs | Recoverable magnetic data | Overwrite for Clear; Purge or destruction when required | Sanitization results or verified destruction | Failed drive or incomplete coverage |
| Optical media | Data on the recording layer | Physical destruction | Inspection and batch record | Recoverable recording surface |
| Removable media | Unknown medium or incomplete sanitization | Identify the medium; sanitize or destroy if assurance is inadequate | Asset-linked results | Unknown medium or failed validation |
| Backup tapes | Recoverable magnetic recordings | Approved degaussing or physical destruction | Equipment check and batch record | Unsupported tape type or ineffective equipment |
Secure Paper and Media Awaiting Destruction
☐ Keep paper and approved media in locked containers and restricted staging areas while they await destruction. Inventory the contents and label containers with tracking IDs - not sensitive details. Separate media that require different destruction methods, and track every movement from release through final disposal.
Check destruction equipment before use, including testing and calibration where applicable. Document on-site destruction or obtain provider evidence linked to the batch. Keep batch IDs and handoff logs for vendor review.
Sanitize Devices and Verify Results
☐ Before release, inventory the storage components covered by policy, sanitize them, and verify the results. Link the sanitization results to the asset ID before releasing the device. Have a separate person perform secondary verification.
Isolate failures and document reprocessing. Escalate missing devices, unidentified media, inaccessible storage, or incomplete evidence.
Plan Deletion of Cloud Data, Backups, and Replicas
☐ Define what deletion must cover. Include provider-held copies, backups, snapshots, replicas, and exports. Work with records management to keep copies subject to retention requirements or legal holds out of disposal batches.
Record the deletion method and any copies that remain. Obtain provider evidence verifying the action, and keep it with the disposal record.
3. Disposal Vendor and Chain-of-Custody Checklist
When you outsource destruction, contract terms and custody records must tie back to the same asset.
Review Vendor Security and Contract Terms
Before a third party handles destruction, check its security controls and the custody trail from pickup to final disposition.
- ☐ Check how the vendor works - not just its certifications. Review background checks, facility access controls, secure transport, and incident reporting. Confirm that certifications cover the facility and services you'll use. Document your review and monitor performance.
- ☐ Put measurable duties in the contract. Name approved subcontractors and downstream facilities. Require written security terms to flow down to subcontractors, while keeping the primary vendor responsible for their actions. Include audit rights and reassess after material changes.
| Control objective | Contract requirement | Retained evidence | Review frequency |
|---|---|---|---|
| Destruction | Follow NIST SP 800-88 Rev. 2 and require verification results | Method specifications, destruction certificates, verification results | Annual or upon material change |
| Downstream facilities | Require prior written approval and written flow-down terms | Subcontractor agreements, facility records | Annual |
| Audit access | Allow inspection of safeguarding policies, procedures, practices, and records | Audit findings and corrective actions | Risk-based |
| Incident reporting | Report successful and attempted incidents promptly | Incident and response records | Each incident |
| Custody exceptions | Investigate missing items, broken seals, count differences, and transfers made without approval | Exception records and closure approval | Per shipment |
| Termination | Require return or destruction of sensitive data; maintain controls for retained copies | Return receipts, destruction evidence, retained-copy exceptions | At termination |
Once the contract is in place, verify each custody transfer.
Track Handoffs and Confirm Destruction
- ☐ Record every custody transfer. Include pickup personnel, dates and times, container and seal numbers, manifests, transport details, receiving facilities, and handoff acknowledgments. Track data-bearing devices by serial number and link each batch to container IDs. Include temporary storage and downstream transfers.
- ☐ Require destruction certificates tied to asset IDs. Each certificate should list the media type, asset IDs or batch IDs, destruction date, method, and final disposition. Match it against the outbound inventory, pickup manifest, vendor intake logs, and applicable sanitization results - not just the shipment total.
- ☐ Keep discrepancies open until evidence resolves them. Investigate missing serial numbers, broken seals, and transfers made without approval. Escalate potential losses through incident response procedures. Periodically select asset serial numbers and request the full pickup-to-destruction record.
Store these vendor records in the disposal file for examiner review.
4. Disposal Records and Examination Readiness Checklist
Once destruction and vendor handoffs are complete, reconcile the records for exam review.
Maintain and Reconcile Disposal Records
Keep one traceable disposal file. Link each asset or batch to its chain-of-custody record, proof of destruction, and final disposition. Record asset or batch IDs, media and data types, approval status, approvers, disposal personnel, destruction location and date/time, method, verification results, and exceptions. Attach source reports, vendor certificates or manifests, incident records, and witness records. Link to source records rather than copying sensitive data.
Before closing disposal, check the file against asset inventories, work orders, and clearance records. Keep retired, in vendor custody, and disposed as separate inventory states. Retirement alone does not mean destruction is complete. Record clearance against the retention schedule and legal hold.
Protect the record set. Use role-based access and least privilege to control who can view or edit records. Organize the files so audit, compliance, and exam teams can retrieve them quickly.
Review High-Risk Batches and Resolve Exceptions
Set written triggers for independent review, including highly sensitive media, failed wipes or purges, and large batches. The reviewer must be separate from the disposal team. Sample retired asset serial numbers and trace each one to its disposal evidence.
Track every exception through closure. If a wipe or purge fails, keep the failure report, evidence of the approved corrective action, and proof of a successful outcome. For missing media, document the incident assessment and reporting outcome. Keep the case open until the reviewer records closure.
5. Conclusion: Approve, Verify, and Document Disposal
Once the checklist is complete, use final approval to close the disposal file. Name one accountable owner and require sign-off from governance, compliance, and IT after retention checks are complete and legal holds are cleared.
Approval should confirm destruction, custody, vendor control, and verification. Update the disposal policy to reference NIST SP 800-88 Rev. 2. If you rely on NAID AAA or R2v3 certification, check that it covers the facility handling the assets.
The destruction certificate is evidence - not the full record. Close the batch only when the vendor’s asset-level destruction report matches the internal inventory. Keep any exceptions open until they’re resolved.
FAQs
How long should we retain disposal records?
Keep disposal records for at least six years to support compliance and provide proof of secure destruction during audits or legal inquiries.
Document a clear chain of custody for each asset, using its serial number to track it from authorization through final disposition. Include records of secure handling and final destruction so you can show what happened long after the assets leave your facility.
What if our cloud provider cannot verify deletion?
Treat deletion as unproven until it can be verified. Before disposing of assets or storage, require documented compensating controls: secure overwriting, degaussing, or physical destruction.
Keep chain-of-custody and disposal records that document authorization, custody and transfer dates, sanitization or removal, and final disposition.
Your contract should specify disposal procedures, security measures that meet or exceed current requirements, and audit or certification evidence. Consider changes to contracts or processes until deletion can be verified.
How do we transition from NIST Rev. 1 to Rev. 2?
Update your media sanitization policy to align with NIST SP 800-88 Rev. 2. Audit your media inventory, then replace generic destruction logs with per-device records that document serial numbers, sanitization methods, verification steps, and operator and witness signatures.
Review vendor contracts to ensure destruction certificates reference Rev. 2. Use quick-reference and crosswalk tools to map your current procedures to the updated requirements. Keep records in one central location, linking each specific asset to its confirmed destruction event.
Related Blog Posts
Get new content delivered straight to your inbox

The Response
Updates on the Reform platform, insights on optimizing conversion rates, and tips to craft forms that convert.

Drive real results with form optimizations
Tested across hundreds of experiments, our strategies deliver a 215% lift in qualified leads for B2B and SaaS companies.
