HIPAA Compliant Forms: Privacy Rule Guide


A form alone cannot make your workflow HIPAA compliant. Before collecting patient information, I check what each field needs, who can access the answers, and where the data goes - even a name tied to an appointment request can be PHI.
My prelaunch checklist covers four areas:
- Data and privacy: Confirm your HIPAA role, limit fields to the task, and separate privacy notices, consent, and any required authorization.
- Access and vendors: Set staff permissions, protect electronic PHI, and confirm vendor terms and any required business associate agreements.
- Daily handling: Assign owners for intake, urgent requests, incident review, retention, and deletion.
- Testing and approval: Use synthetic data to check every destination, record approval, and review changes before they go live.
<u>Don’t collect PHI until those checks are complete.</u> For Reform, that includes verifying the plan, terms, and BAA scope. Keep required HIPAA documentation for six years from creation or last effect, whichever is later - not as a blanket rule for all patient records.
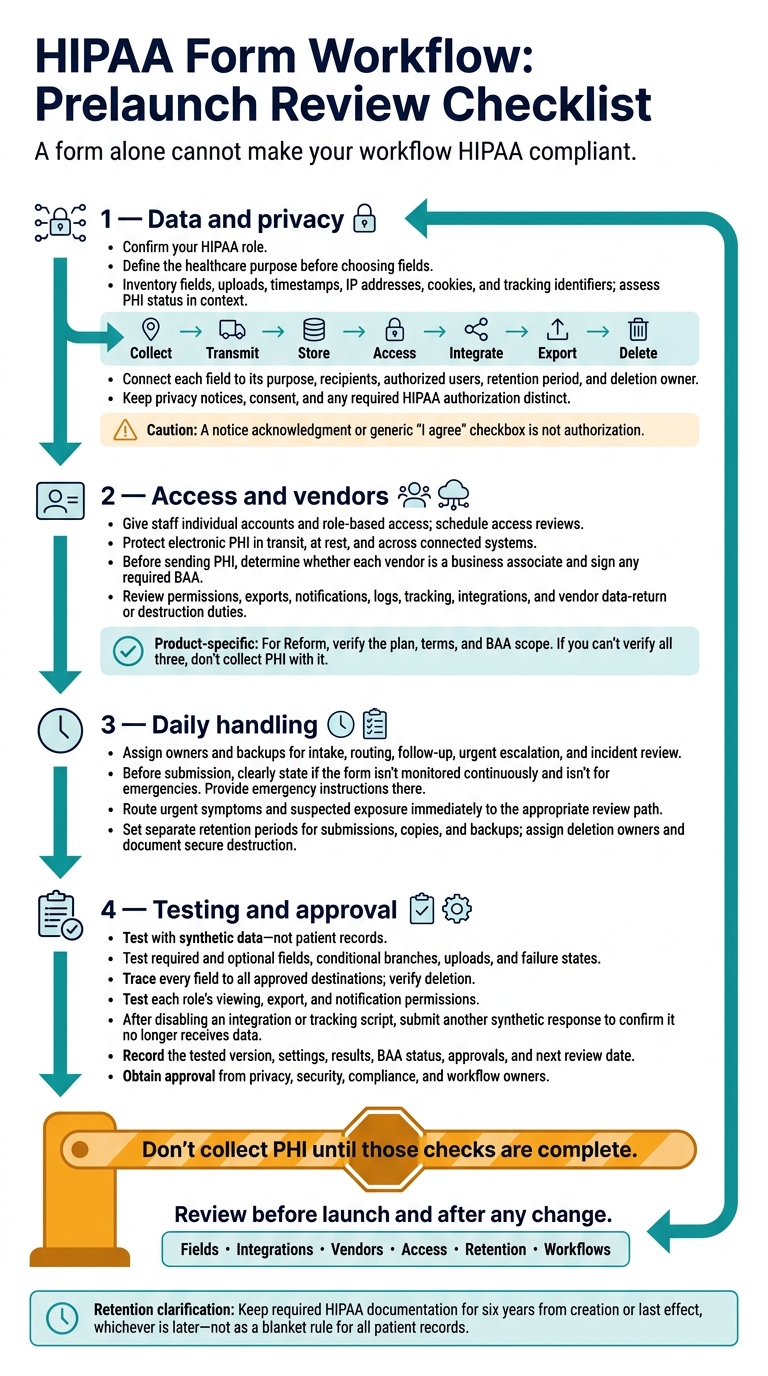
HIPAA Form Workflow: Prelaunch Review Checklist
Map Form Data, Choose Fields, and Explain Privacy
Once you identify PHI, connect each field to a workflow, recipient, and retention rule. Define the healthcare purpose before choosing fields.
Scheduling and clinical intake require different data. An appointment request may need only a name and contact method; it can still contain PHI. Detailed history belongs in clinical intake, not the first request unless care requires it.
Map Every Field and Data Destination
Inventory every field, upload, timestamp, IP address, cookie, and tracking identifier. Determine PHI status based on context, including technical identifiers linked to a healthcare request. Trace where data is collected, transmitted, stored, accessed, integrated, exported, and deleted. Record the actual destinations and retention periods.
The following examples illustrate field-level decisions; replace destinations and retention periods with those approved for your workflow.
Field name Purpose PHI status Required status Destination Authorized users Retention period Deletion owner Patient name Identify requester Yes Yes EHR / CRM Front desk, clinical staff 7 years Privacy officer Contact number Contact Yes Yes CRM Front desk 7 years Privacy officer Clinical history Support care Yes Only when clinically needed EHR Clinical team 7 years Clinical lead IP address Security Potentially, when linked to a healthcare request Auto Server logs IT admin 30 days IT manager
Ask Only for Data the Workflow Needs
Collect only what the workflow needs. Use structured choices and conditional fields rather than broad prompts such as “Tell us everything.” Ask for diagnoses, medications, insurance details, or other sensitive information only when the workflow calls for them.
HIPAA’s minimum necessary standard is not a blanket rule for every treatment-related collection. It does not apply to disclosures to, or requests by, a health care provider for treatment. Keep marketing-only questions separate and optional. Don’t put sensitive answers in URLs, analytics events, or unencrypted confirmation emails.
Once you’ve mapped the fields, write patient-facing language that explains how you’ll collect and use the information.
Distinguish Notices, Consent, and HIPAA Authorization
Explain why you collect information, how you’ll use it, who receives it, which fields are required, and how patients can contact the privacy office.
Permitted treatment, payment, and healthcare operations generally do not require HIPAA authorization. When authorization is needed, use a separate document or a distinct section. A notice acknowledgment or generic “I agree” checkbox is not authorization. Keep these records separate:
| Document | Purpose | Applicability | Records to retain |
|---|---|---|---|
| Intake consent | Permission to provide routine treatment and bill insurance | Standard for new patient registrations | Signed consent form |
| Notice of Privacy Practices acknowledgment | Document receipt of the privacy notice | Direct treatment providers generally must make good-faith efforts to obtain acknowledgment at first service, subject to exceptions | Acknowledgment or documented attempt |
| Optional communications consent | Permission to contact via SMS or unencrypted email | Optional; based on patient preference | Opt-in/opt-out record and timestamp |
| HIPAA authorization | Permit a specified use or disclosure not otherwise allowed by the Privacy Rule | Required when no other Privacy Rule permission applies | Signed authorization and revocation records |
A valid authorization must identify the information, the people authorized to disclose it, the recipients, the purpose, an expiration date or event, and the individual’s signature and date. If a representative signs, describe their authority.
Include the right to revoke in writing, a notice about possible redisclosure by recipients, and statements explaining whether treatment, payment, enrollment, or benefits can depend on signing. Retain required HIPAA documentation for six years from creation or last effect, whichever is later. That period does not automatically apply to every patient record.
sbb-itb-5f36581
Manage Access, Integrations, and Intake
Once you’ve mapped the fields and destinations, set controls for who can view the data and where it goes.
Limit Staff Access and Review Vendors
Give each staff member their own account, with access based on their job. Schedule access reviews and limit permissions to the fields and destinations you’ve mapped. Protect PHI in transit, at rest, and across every connected system.
Before sending PHI, determine whether each vendor is a business associate and sign any required BAA. Review permitted uses, safeguards, incident reporting, subcontractor obligations, and duties for returning or destroying data. Check the actual configuration - not just the certification.
Review every system that receives submission data or could expose it.
| Connected system | PHI exposure to check | Access needs | BAA determination | Settings to review | Approval owner |
|---|---|---|---|---|---|
| CRM | Patient details and submitted data | Role-based access | Yes | Permissions, exports, activity logs | Privacy/compliance officer |
| Scheduling | Appointment details | Limited access for admin and clinical staff | Yes | Calendar visibility, reminders | Operations manager |
| Email/notifications | Message bodies and attachments | Restricted recipients | Yes | Encryption | IT/security manager |
| Storage/cloud | Submissions and attachments | Admin-only access | Yes | Sharing, encryption, retention | IT director |
| Analytics | Behavioral data only, when de-identified | Aggregated access | No, if data stays de-identified | Field capture, identifiers, session recording | Data privacy lead |
| Automation/APIs | Data flow and payloads | System-level access | Yes | Logging and credentials | Systems architect |
| Support/chat | User queries and attachments | Support staff only | Yes | Ticket visibility and attachments | Customer success lead |
Assign Intake, Routing, and Escalation Roles
Assign an owner and a backup for every step in the intake process. Set response times staff can meet, and train them on the workflow before granting access.
| Step | Responsible role | Response time | Channel and safeguard |
|---|---|---|---|
| Submission | Patient/user | Real-time | HIPAA-compliant form; encryption at rest and in transit |
| Triage | Intake coordinator | Within 2 hours | Secure dashboard; role-based access control |
| Routing | Systems admin | Instant | API or CRM sync; audit logging |
| Follow-up | Clinical staff | Within 24 hours | Secure portal or encrypted email with identity verification |
| Urgent escalation | On-call clinician | Immediate | Secure phone or page; emergency protocols |
| Incident review | Privacy officer | Within 1 hour | Internal secure log; breach assessment |
| Deletion | Data steward | Per schedule | Automated deletion; verified secure destruction |
Before submission, clearly state if the form isn’t monitored continuously and isn’t for emergencies. Provide emergency instructions at that point, too.
Route urgent symptoms to the on-call clinician immediately. Escalate suspected exposure right away for review and any required notification.
After assigning the workflow, test the form builder and every connected path before launch.
Set Retention and Deletion Schedules
Set separate retention periods for submissions, copies, and backups. Assign a deletion owner and review date, confirm vendor deletion duties, and document secure destruction using NIST 800-88 guidance.
Review the Form Builder and Test Before Launch
Check Reform’s Fit for Your Data
Once you’ve mapped fields, roles, and retention, test the live form before launch. Before collecting PHI with Reform, confirm its plan, terms, and BAA scope. If you can’t verify all three, don’t collect PHI with it.
Test every field path and connected system, including disabled features. Even a basic healthcare contact form can collect PHI. Review analytics, tracking, validation, and integrations to check what data each feature collects and sends during testing.
Test Fields and Data Flows
Test with synthetic data - not patient records. Check required and optional fields, conditional branches, uploads, and failure states. Follow each field’s data to every approved destination and connected system. Verify that deletion works as configured.
Sign in under each role. Check what that role can see, export, and receive against its approved role-based access. Review notifications, exports, logs, and scripts for PHI exposure. After disabling an integration or tracking script, submit another synthetic response to confirm it no longer receives data.
Record Approval and Review Changes
Keep a dated launch record with the tested version, settings, results, BAA status, approvals, and next review date. Include the mapped system’s plan terms and retention settings.
Confirm that notices and any required authorizations match actual data use. Record approval from privacy, security, compliance, and workflow owners. Reopen the review whenever fields, integrations, vendors, access, retention, or workflows change.
Conclusion: HIPAA Form Review Checklist
Review these four areas before launch and after any change.
- Role and data: Confirm your HIPAA role. Map every field from form entry through storage, export, and deletion. Keep only fields that support a defined workflow.
- Privacy and access: Check required notices, authorizations, staff access, BAAs, integrations, incident notifications, and exports.
Next, assign responsibility for the day-to-day work.
- People and procedures: Name owners for intake, incident notifications, exports, retention, and deletion. Document training and incident response.
- Launch and review: Keep test records and approvals, and maintain a process for reviewing changes.
Rerun the review whenever any part of the workflow changes. Form features help, but they do not make a workflow HIPAA compliant.
FAQs
How do I know if HIPAA applies to my forms?
HIPAA applies if your form collects, stores, or transmits protected health information (PHI): information that identifies a person and relates to their health, healthcare, or payment for care [2][3].
Check whether your form connects any of HIPAA’s 18 personal identifiers - such as names, contact details, or birthdates - to health information. If it does, the Privacy and Security Rules apply [2][3][4].
What if a patient submits sensitive information I didn’t request?
Treat the information as Protected Health Information (PHI) and follow your existing security protocols for access controls, encryption standards, and audit logging.
To reduce repeat incidents, replace open-text fields with structured inputs, such as dropdowns, radio buttons, or checkboxes. Add help text next to these fields telling patients not to enter clinical details at this stage.
How do state laws affect my form retention schedule?
HIPAA requires keeping certain compliance records for at least six years, but it doesn’t set a blanket six-year rule for all audit logs. State laws may require longer retention for some records - sometimes 10 years. Check both federal and state rules when setting retention periods, and follow the strictest applicable requirement.
Use regular risk assessments to identify state-specific requirements and update internal recordkeeping policies so form submissions and audit logs meet the rules that apply.
Related Blog Posts
Get new content delivered straight to your inbox

The Response
Updates on the Reform platform, insights on optimizing conversion rates, and tips to craft forms that convert.

Drive real results with form optimizations
Tested across hundreds of experiments, our strategies deliver a 215% lift in qualified leads for B2B and SaaS companies.
