

Sensitive Data Sharing Under CCPA: Checklist


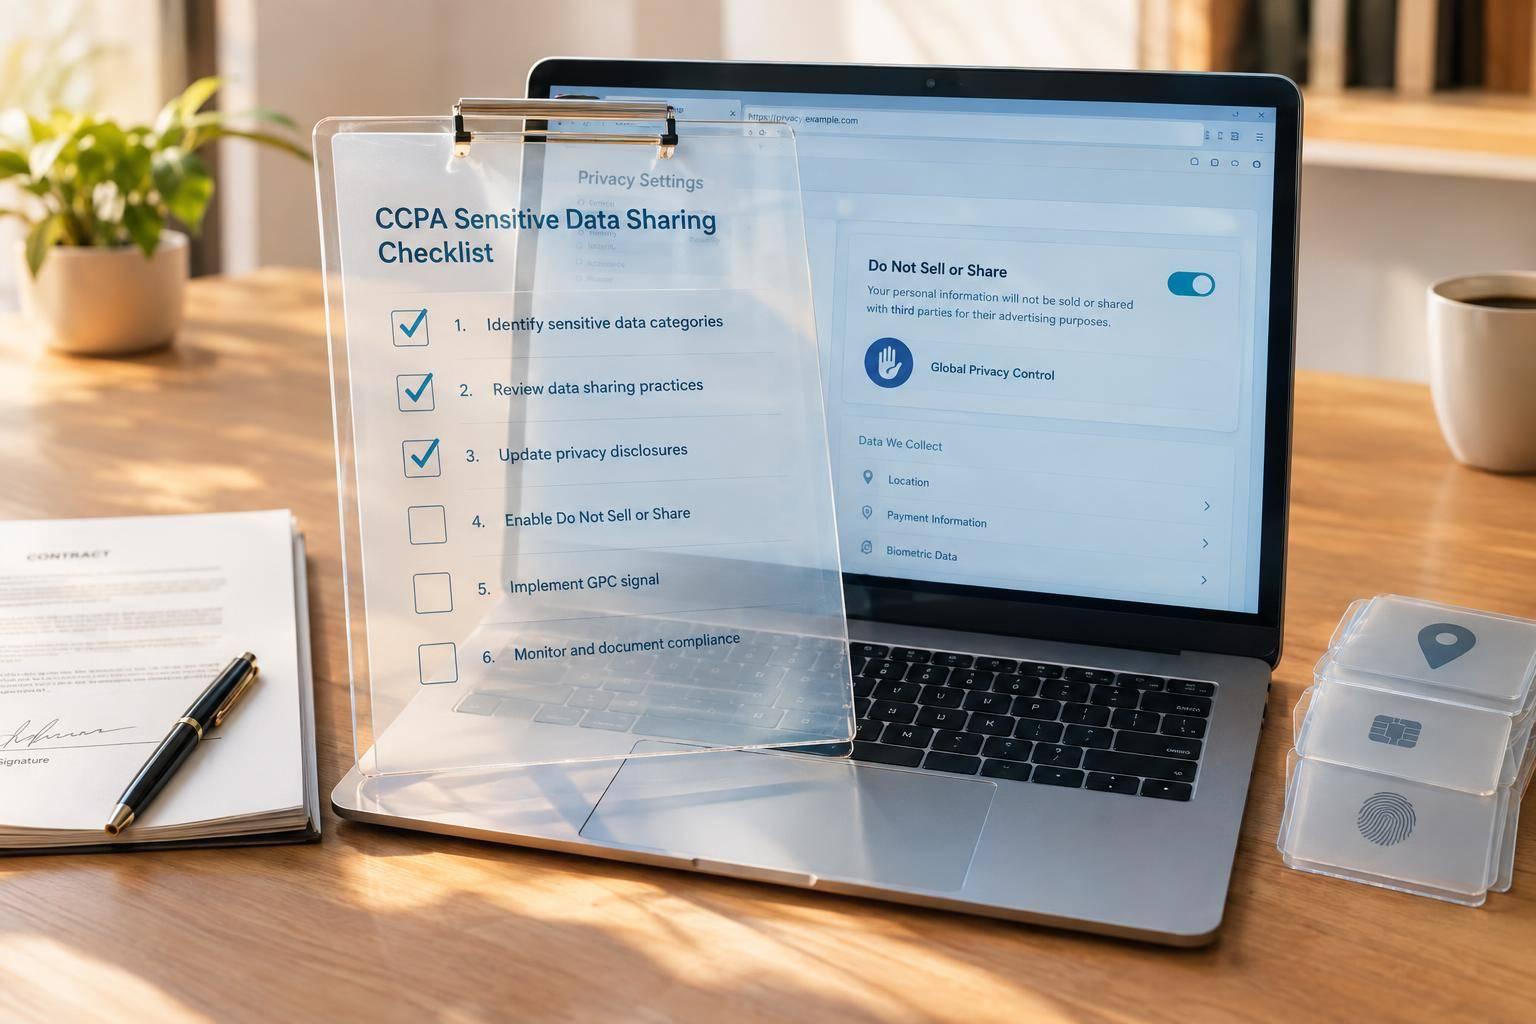
Before I launch optimized conversion forms with sensitive fields, I check what it collects, where the data goes, and whether privacy choices work. Under CCPA, “sharing” means disclosure for cross-context behavioral advertising - not every vendor transfer.
I use 6 checks to review the form before launch:
- Confirm CCPA coverage and map each field and recipient.
- Remove unneeded sensitive fields; document purposes, retention, and notices.
- Classify recipients and check contracts and downstream restrictions.
- Restrict access and test what integrations actually send.
- Test sale/sharing opt-outs, Global Privacy Control, and any applicable sensitive-data limits.
- Record approval, assign fixes, and review again when something changes.
My rule: <u>no approval until the required controls work</u>. A policy alone isn’t enough - I need test results showing that choices reach the systems receiving the data.

CCPA Sensitive Data Sharing: 6 Prelaunch Checks
Identify Sensitive Fields and Their Purposes
Review Fields, Uploads, and Free Text
Check the current statutory categories: government identifiers; account credentials; precise geolocation within 1,850 feet; race or ethnicity; religious or philosophical beliefs; union membership; genetic data; biometrics used for identification; health data; sex life; sexual orientation; and mail, email, or text contents unless the business is the intended recipient.
Review uploads, hidden values, auto-collected location data, and free-text responses. Remove prompts that ask for sensitive details you don’t need. Optional fields still count as collection.
Record Field Purposes and Retention Periods
Give every field you keep a specific purpose. Remove fields you don’t need for the service or response - even optional ones. Check that collection, use, retention, and disclosure are reasonably necessary for the stated purpose.
Use these checks to complete a record for each field.
Sensitive field Collection purpose Recipient Retention period Choice requirement Deletion method Precise geolocation Service delivery Logistics partner Document the service-linked period or criteria Right to Limit Session-based deletion Government identifier Identity verification Internal / KYC provider Document the necessary period and any legal retention requirement Right to Limit Manual/API Account login plus password or security code Authentication Internal Until account closure Security exception User-initiated
Make sure the notice matches what you collect. At or before collection, disclose the sensitive categories, purposes, sale/sharing status, and retention periods or criteria. Replace “as needed” with a specific period or trigger. Send any incompatible new uses for privacy review before launch.
sbb-itb-5f36581
Classify Recipients and Check Contracts
Use the field map to classify each recipient before any transfer goes live.
Determine Each Recipient’s CCPA Role
Record each recipient, the fields it receives, and its CCPA role. Keep its location, access method, subprocessors, retention, and contract status in the data map. “Vendor” is a procurement label - not a CCPA role. Classify each relationship based on the signed contract and what the recipient actually does.
Use this table to match each recipient with the right contract and controls.
| Recipient classification | Permitted purpose | Contract requirements | Sale/sharing assessment | Required controls |
|---|---|---|---|---|
| Service provider | A specific business purpose for the business | Written terms must identify limited purposes, prohibit sale/sharing, restrict other uses, and address required privacy obligations | Excluded from sale/sharing only when both the contract and actual practices meet CCPA requirements | Enforce purpose and data-combining restrictions |
| Contractor | A specific business purpose under the business’s direction | Written terms must impose service-provider-style restrictions and controls | Do not rely on the label alone; verify the contract and actual practices | Verify required compliance certification |
| Third party | Processing outside qualifying service-provider or contractor restrictions | Review required contract protections; a generic vendor agreement is not enough | Assess whether the disclosure is a sale or sharing, including cross-context behavioral advertising | Apply applicable sale/sharing opt-outs |
Test sale and sharing separately. Flag money, valuable consideration, cross-context behavioral advertising, and recipients’ use of submissions for their own commercial purposes. Also flag dataset combining: a free integration is not automatically exempt. Send unresolved disclosures for further review.
Check Contract Terms and Onward Transfers
Verify enforceable limits. Service-provider and contractor terms should specify services and purposes, prohibit sale/sharing, restrict use outside the direct business relationship, and address data combining. Check for privacy safeguards, consumer-request assistance, deletion or return, monitoring and remediation rights, and notice if compliance becomes impossible. Review applicable third-party contract duties separately.
Approve downstream recipients before enabling transfers. Require equivalent written restrictions, oversight of downstream recipients, and downstream deletion controls before approval. Record approved purposes and fields, review dates, and any change-notice or objection arrangements. Do not approve an onward transfer if its purpose or protections remain unclear.
Restrict Integration Data and Submission Access
Allowlist fields and test actual payloads. Check sensitive and hidden fields, uploads, internal notes, conditional answers, and abandoned submissions across webhooks, notifications, logs, and connected records.
At each destination, verify least-privilege access, multifactor authentication, encryption, retention, and deletion. Keep field mappings, test evidence, the approver’s name, and the review date. Carry unresolved sale/sharing questions into the consumer-choice test.
Test Consumer Choices Across Systems
Verify that approved consumer choices stop downstream transfers as intended.
Check Opt-Out and Sensitive Data Limits
- [ ] Check sale/sharing choices. Provide a clear sale/sharing opt-out and honor Global Privacy Control (GPC). Test links in all major browsers. Don’t require an account or burdensome identity verification to opt out.
- [ ] Assess sensitive personal information limits separately. Check whether its use or disclosure goes beyond reasonably expected purposes. If the right to limit applies, provide a separate “Limit the Use of My Sensitive Personal Information” mechanism.
- [ ] Check required consent. Require opt-in consent for sale or sharing involving consumers under 16. Block preselected choices and other dark patterns.
Test Requests and Log Results
Trace separate opt-out, GPC, and sensitive-data-limit test requests from start to finish through the same multi-step form, CRM, marketing, enrichment, and analytics paths mapped earlier. Confirm that restricted transfers stop and that the limit signal reaches every downstream system. Log each system touched, the test result, the fix date, and the retest date.
Conclusion: Record Approval and Fix Gaps
Once the checklist is complete, record final approval and close any gaps. Approve only after the field map, recipient review, contract checks, and choice tests are complete.
Assign Fixes and Set Review Triggers
Record the reviewer, approval date in MM/DD/YYYY format, form/workflow version, approved fields and recipients, purposes, retention, contract references, consumer-choice test results, evidence links, open issues, and final status. Link to the earlier field map, contract review, and test evidence.
Check that the prefilled forms, inventory, policy, notice, contracts, logs, and integration settings match. Give each gap an owner, due date, and retest step. Block launch or pause the affected transfer if it lacks any of the following: a documented purpose that matches the notice, required notice, contract coverage, downstream transfer restrictions, or a working consumer-choice control.
Set a periodic review date, and use it as the next change trigger. Start a new review whenever fields, purposes, vendors, contracts, retention, or workflows change - or a choice test fails. Reapprove the affected fields and recipients rather than relying on the original sign-off.
FAQs
How do I know if CCPA applies to my forms?
The California Consumer Privacy Act (CCPA) applies to your forms if your organization meets the legal threshold for a covered for-profit business that collects California residents’ personal information.
That includes forms that collect identifiers - such as names, email addresses, IP addresses, or cookie IDs - and later share them with third parties for cross-context behavioral advertising, retargeting, or lead enrichment.
Does collecting sensitive data always trigger the right to limit?
No. Under the CCPA, collecting sensitive personal information alone does not trigger the right to limit its use or disclosure. That right generally applies when a business uses or discloses the information beyond permitted purposes.
The rights to opt out of sale or sharing are separate. They may apply to cross-context behavioral advertising or transfers to recipients without proper service-provider restrictions. Transfers confined to authorized business purposes under secure, compliant contracts may not trigger those opt-out rights.
What should I do if a vendor ignores opt-outs?
If a vendor can’t honor opt-out requests, they likely don’t qualify as a CCPA service provider. Start by reviewing your data processing agreements. They should prohibit selling or sharing personal information and require the vendor to comply with opt-out requests.
If the vendor still can’t comply, reclassify the transfer as a sale or share and update your public disclosures. Consider limiting or stopping data flows to prevent processing that isn’t permitted.
Related Blog Posts
Get new content delivered straight to your inbox

The Response
Updates on the Reform platform, insights on optimizing conversion rates, and tips to craft forms that convert.

Drive real results with form optimizations
Tested across hundreds of experiments, our strategies deliver a 215% lift in qualified leads for B2B and SaaS companies.
